Newsletter
Riding cloud can be tricky, don’t fall from it, in the weekly cyber !
Somehow short week for me, but quite intense, ended escaping in the hoods off grid, and that’s pretty good !
Meanwhile, earlier, this week has been quite intense, and despite my good will, humanity always find way to show how bad and nasty it can be, and as bad as I want to expose stupidity, it will not help, because it seems some are so bad, that there is no cure. For these, R.I.P means Rot In Peace :D
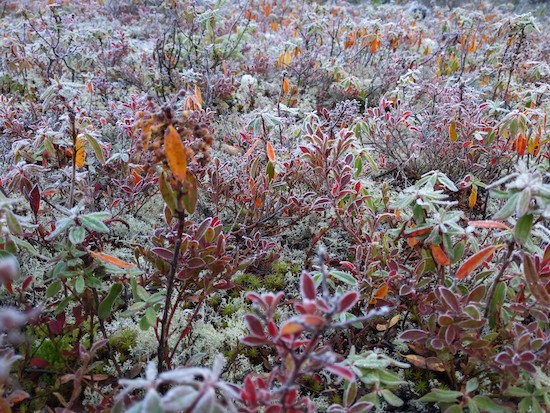
BUT FOR YOU, 48K+ followers, 24K+ subscribers to this newsletter, I send you all my love, and the peace I found in nature, here, north from Quebec in the « Parc des Grands Jardins », where you wake after a cold night in beautifully frozen nature, that quickly transform as the sun rises !

Back to our topic, this week in 46 points, this happened :
1 – Scammers strategy reviewed, as they use porn scam to get your attention – Porn Spam, Malware and Questionable References to Teens
2 – I told you, they just went on vacation ! And now they are fully back ! REvil ransomware is back in full attack mode and leaking data
3 – Some said it’s great, I believe, in the case of this Facebook based service, a backup encrypted with a password stored in the cloud, is not something safe, how long will this backup hold against dictionary attack based on all the passwords ever leaked on internet ? 10 seconds ? WhatsApp to Finally Let Users Encrypt Their Chat Backups in the Cloud , good idea, but I’m afraid it’s a false sense of privacy.
4 – The cloud strikes again ! (I know you come from my cloud rants :P ) – MyRepublic Data Breach Raises Data-Protection Questions
5 – This article bring facts you must be aware of so as you avoid the pitfalls – cloud-based issues comprise 79% of observed exposures compared with 21% for on-premises assets ( I see you cloud lover, bla bla, this sentence is out of context, bla bla… ok, read the linked article on the post, and you’ll have all the context :) )
6 – Wireless is weak, bluetooth hacked again – BrakTooth Vulnerabilities Riddle Bluetooth Devices From Numerous Vendors
7 – Zero day exploit out and shared. No patch, no fix. Windows MSHTML zero-day exploits shared on hacking forums (more in the comments of the post as usual)
8 – How much do you know who’s really behind the keyboard ? Real-Time Identity Protection at Last: Closing a Critical Gap in our Security Stacks
9 – Once again, don’t fall for the scam – FTC warns of extortionists targeting LGBTQ+ community on dating apps
10 – Everything is fake in technology, and it’s very challenging to know what is a good investment and what is not (like if it took human model ! ). Fake Walmart press release hoax causes Litecoin to spike 34%
11 – You are hacked and you don’t know it yet – Linux Implementation of Cobalt Strike Beacon Targeting Organizations Worldwide
12 – Hopefully you’ll update your build quickly, but won’t drop security scans to avoid supply chain attacks – Critical Bug Reported in NPM Package With Millions of Downloads Weekly
13 – Do you have an incident response plan ? ( hint : you must have one) – BlackMatter ransomware hits medical technology giant Olympus
14 – A not so sandboxed browser tab (deception again I know) – New SpookJS Attack Bypasses Google Chrome’s Site Isolation Protection
15 – On a related topic, the not so #privacy focused browser needs patching – Google patches 10th Chrome zero-day exploited in the wild this year (Security and privacy are two very different things ! )
16 – Windows 11, lol – Firefox now bypasses Windows 11’s messy default browser settings (yet they are about to sign a deal with Microsoft to make Bing the default search engine….. that makes you wonder)
17 – Apple patch time ! There is a worm in the apple – Apple products vulnerable to FORCEDENTRY zero-day attack – patch now (if you haven’t patched at this time, shame on you ! )
18 – HP Omen patch time (HP Gaming PC line) – HP OMEN Gaming Hub flaw hits millions of gaming devices
19 – Always watch where you download from, as once again threat actor use ads to be placed on top of search results – New Stealthier ZLoader Variant Spreading Via Fake TeamViewer Download Ads . That said, using pihole instance as your DNS server should wipe all ads from your web browser, and drop the risk :P
20 – The evolution of ransomware, from early days to industrial infrastructure take over – Ransomware, a timeline of destruction Part II
21 – We often say the perimeter is gone, but it doesn’t mean your attack surface is gone, it’s actually expended and on steroid if you use the cloud – Principles Of External Attack Surface Protection: Discover Everything
22 – Top of the risks being the dangerous cloud and an ever growing uncontrolled attack surface. No wonder why data continuously leak – Most Fortune 500 companies’ external IT infrastructure considered at risk
23 – A very accurate view, explaining why it takes an incident for organization to handle their security posture properly – Ransomware preparedness is low despite executives’ concerns
24 – Don’t forget to register for the coming event on Sept 24th, great panels covering the ransomware challenges, and what we can do about it – I’m lucky to participate in 2 panels, with amazing co-panelists, and this will be quite fun and interesting – Was so sick during the preparation of this one, you have no idea :P
25 – This article in PDF format will cover some key points of supply chain security, and what to look after – How safe is your technology supply chain
26 – Oldie and still goodie – How to Install Fail2ban on Rocky Linux and AlmaLinux
27 – Cloud is poisoning your VMs. Want it or not. Issue with the cloud, you control nothing (Yeah admit it, you missed these ones :P ) – Microsoft Azure Users with Linux VMs Exposed to Security Vulnerabiltiy Called OMIGOD—How to Fix
28 – You’d better be sure that the channel you pick as replacement for the password is as safe as the password ! Sensitive topic to me, I don’t think passwordless is a fix, password is supposed to be a secret, if no longer a secret, then there is no confidentiality, see what I mean ? If you need third party to support the validation of you, this is becoming to be complex – Microsoft rolls out passwordless login for all Microsoft accounts (lots of comments on this post, some pros, some cons).
29 – Packets Can Cause Bullets – Why cyber wars becomes war
30 – Great news for previous Revil victims ! (assuming you kept a copy or image of your encrypted drives) – Free REvil ransomware master decrypter released for past victims
31 – Hopefully by now, all your NETGEAR manageable switched are patched ! Third Critical Bug Affects Netgear Smart Switches — Details and PoC Released
32 – The whole internet relies on pretty weak bases, one being domains – Anonymous Hacker claims to have stolen Data from Epik
33 – A vulnerability is a risk only if there is a way to exploit it – No Patch for High-Severity Bug in Legacy IBM System X Servers – Micro network segmentation ant ZTNA for the rescue !
34 – Everyday we help customers effectively protecting their infrastructure. Have started to take care of your security ? (selft push for the work side at VARS :D ) – Ransomware encrypts South Africa’s entire Dept of Justice network
35 – Don’t let your router serve evil ! MikroTik shares info on securing routers hit by massive Mēris botnet
36 – Don’t wait to reach that point ! Prevention ! Ransomware gang threatens to wipe decryption key if negotiator hired
37 – Smart is dumb, not the first time I say it, if it contains the word « smart » in its name, you are not the smart part of it ! Smart Home Hack Breaks Down Walls Figuratively And Literally
38 – Nice article, points and puns, showing that there is still a threat for low hanging fruits – Airline Credential-Theft Takes Off in Widening Campaign
39 – Running windows on Linux is way less dangerous than the opposite :) the underlaying systems should be the reliable one :) New malware uses Windows Subsystem for Linux for stealthy attacks
40 – I have to admit, it has been couple of weeks since the last joke like this – New Windows security updates break network printing
41 – How much would it take to bribe your low paid employees for their access ? AT&T lost $200M in seven years to illegal phone unlocking scheme
42 – As usual, keep your systems patched, and apply one of the oldest security principle, least privileges. Nowadays in an hyper connected and infected cyber world, it would not be very wise, to say the least, to let any user with full power on a systems, or even not patching properly – Capoae Malware Attacking Linux systems & Web Apps Using Multiple Vulnerabilities
43 – While you should have active patch management, these should not be missed ! Researchers compile list of vulnerabilities abused by ransomware gangs
44 – The more we place services online, the more we grow our attack surface – Cyberattack hits German Election body
45 – This might actually be effective – U.S. to sanction crypto exchanges, wallets used by ransomware
46 – An interesting reading to start the week – Security Implications of a weakened supply chain
Wishing you a great week all, as you can see this newsletter went out late sunday night :D Hopefully it will bring some useful points to you ! Good night (Or good day if you read this in the morning :) )

Pages
- À propos
- Alexandre Blanc Experience or work background
- Connected=hacked, cloud=leak, why
- Keeping track for my speaking events / appearances
- My take on Zero Trust – SP 800-207
- Openvpn and pihole on OVH VPS Server FAQ
- Raspberry 3 router project FAQ
- Spotting LinkedIn fake profiles, the tail of industrial spying, should I trust this contact ?
Search this Site
Archive
- août 2026
- avril 2025
- juin 2024
- mai 2024
- mars 2024
- février 2022
- janvier 2022
- octobre 2021
- septembre 2021
- mai 2021
- octobre 2020
- juin 2020
- avril 2020
- avril 2019
- janvier 2019
- juin 2018
- mars 2017
- octobre 2016
- août 2016
- mai 2016
- septembre 2015
- mai 2015
- février 2015
- novembre 2014
- septembre 2014
- août 2014
- janvier 2013
- décembre 2012
- juillet 2012
- janvier 2012
- novembre 2011
- octobre 2011
- mai 2011
- avril 2011
- mars 2011
- février 2011
- janvier 2011
- décembre 2010
- novembre 2010
- octobre 2010
- septembre 2010